Product
Static outbound IP proxy features
Fixedmark gives your serverless or PaaS app a pair of static outbound IPs through one proxy URL. It supports HTTP CONNECT over TLS, SOCKS5, and a tunnel CLI, with connection logs and per-token destination allowlists. Fixedmark is in early access: every feature marked Early access is built, and the roadmap lists only what is not built yet.
Built
Available in early access
Built and running for early-access accounts, and part of the first public version.
- Early access
Dedicated IP pairs
Two static IPv4 addresses reserved for your account only, load-balanced for high availability. Allowlist both once.
- Early access
HTTP, HTTPS, and SOCKS5 in one plan
HTTP CONNECT for APIs and SOCKS5 for databases, SSH, and any TCP service. One subscription, one set of IPs.
- Early access
Zero-knowledge by default
TLS passes through end to end and is never decrypted. The TLS proxy endpoints, port 443 for HTTP and 1443 for SOCKS5, keep your proxy credentials encrypted. The plain 8080 and 1080 endpoints, for clients that cannot do TLS, send them in cleartext, so use TLS or fm tunnel where you can.
- Early access
Regions near your APIs
Singapore, Newark, and Ashburn, plus Mumbai in India. Put your IPs next to the database or API you call.
- Early access
Connection logs
See destination, SNI, bytes, egress IP, and result for every connection, so allowlist errors are easy to debug.
- Early access
Destination allowlists
Restrict each token to the hosts and ports it needs, such as api.razorpay.com:443. A leaked token cannot reach anything else.
- Early access
fm tunnel CLI
Forward local ports to IP-restricted databases for drivers without proxy support. Works from a local config file with no startup API call.
- Early access
Usage alerts and webhooks
Soft limits with alerts before you hit them, plus webhooks for quota and IP health events.
- Early access
REST API, fm CLI, and API keys
Create apps, order IPs, and rotate credentials from the fm CLI or the REST API with org API keys. fm api calls any route in the API reference.
- Early access
Members, teams, and SSO
Invite people with roles such as admin, developer, billing, and viewer, give teams access app by app, and sign in through your identity provider on plans with SSO.
- Early access
Tunnels
Give partners a hostname on port 443, or a TCP port, that reaches a service on your machine through fixedmarkd. TLS passes through end to end, and two shared ingress IPs on two nodes keep the hostname up when one fails. Included on Pro and up. A dedicated inbound IP is an add-on at $9 per IP-month, billed by the hour.
In the dashboard
See the pair and every connection
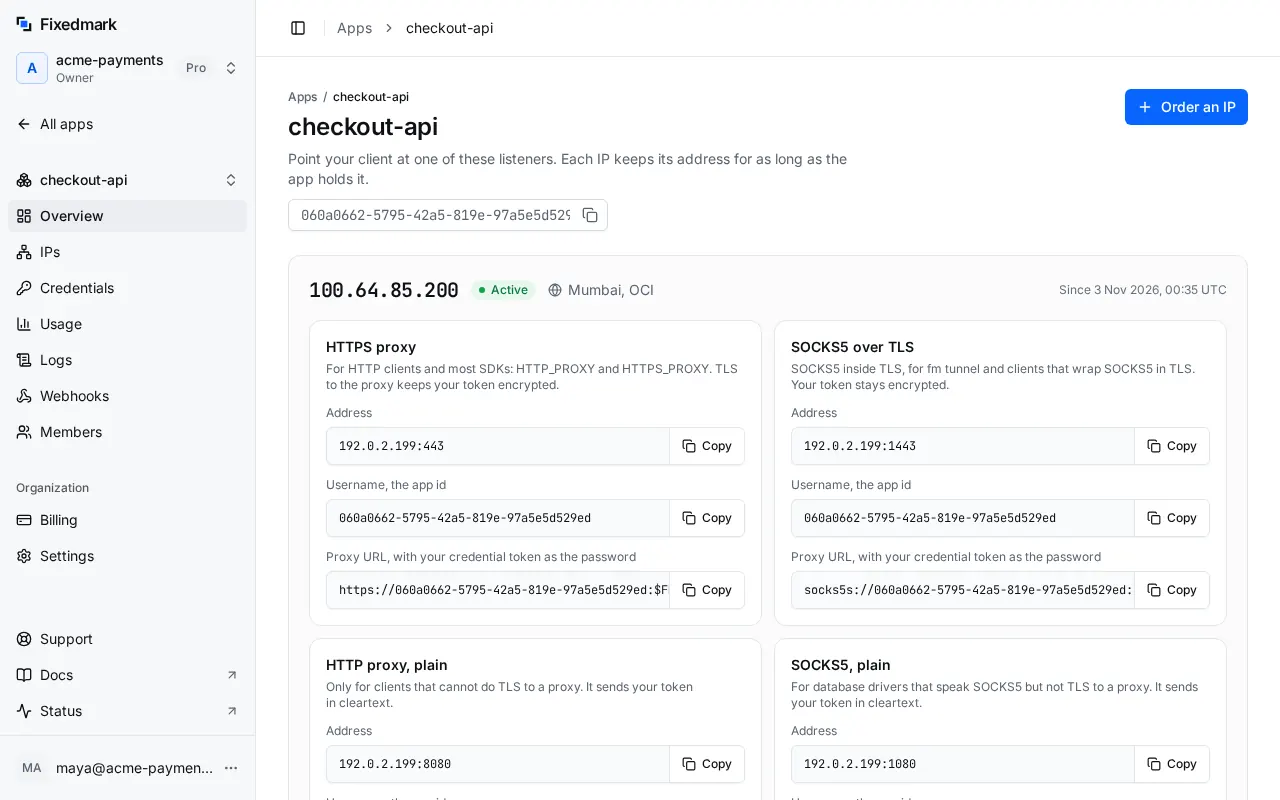
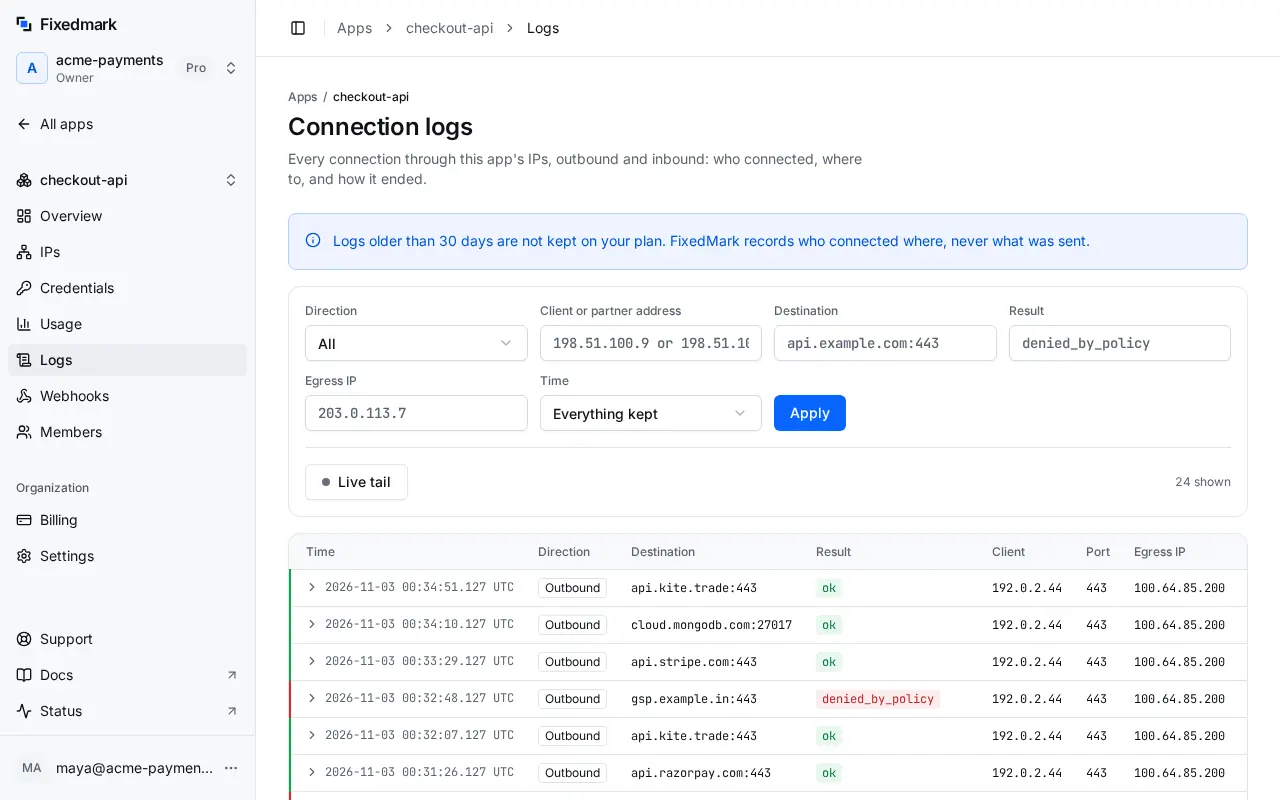
Screens from the Fixedmark dashboard: an app's IP pair, and the connection log that shows which address each request left from.
Dedicated IP pairs
Two static IPv4 addresses reserved for your account only, load-balanced for high availability. Allowlist both once.
- Each IP shows its address, region, and cloud
- HTTPS proxy on port 443 and SOCKS5 over TLS on 1443, each with a copy button
- A curl line that prints the address your partner will see
Connection logs
See destination, SNI, bytes, egress IP, and result for every connection, so allowlist errors are easy to debug.
- Destination, result, bytes, client, and egress IP for each connection
- Filters for direction, address, destination, result, and time, plus a live tail
- Who connected where and how it ended, never what was sent
Inbound
Tunnels
Tunnels on Pro and up, with a dedicated inbound IP as an add-on at $9 per IP-month, billed by the hour. Partners reach a service on your machine by hostname on 443, or by TCP port, through two shared ingress IPs on two nodes, and no Fixedmark node terminates the partner's TLS. Set up a tunnel. Need an address of your own? Add a dedicated inbound IP.
No public IP
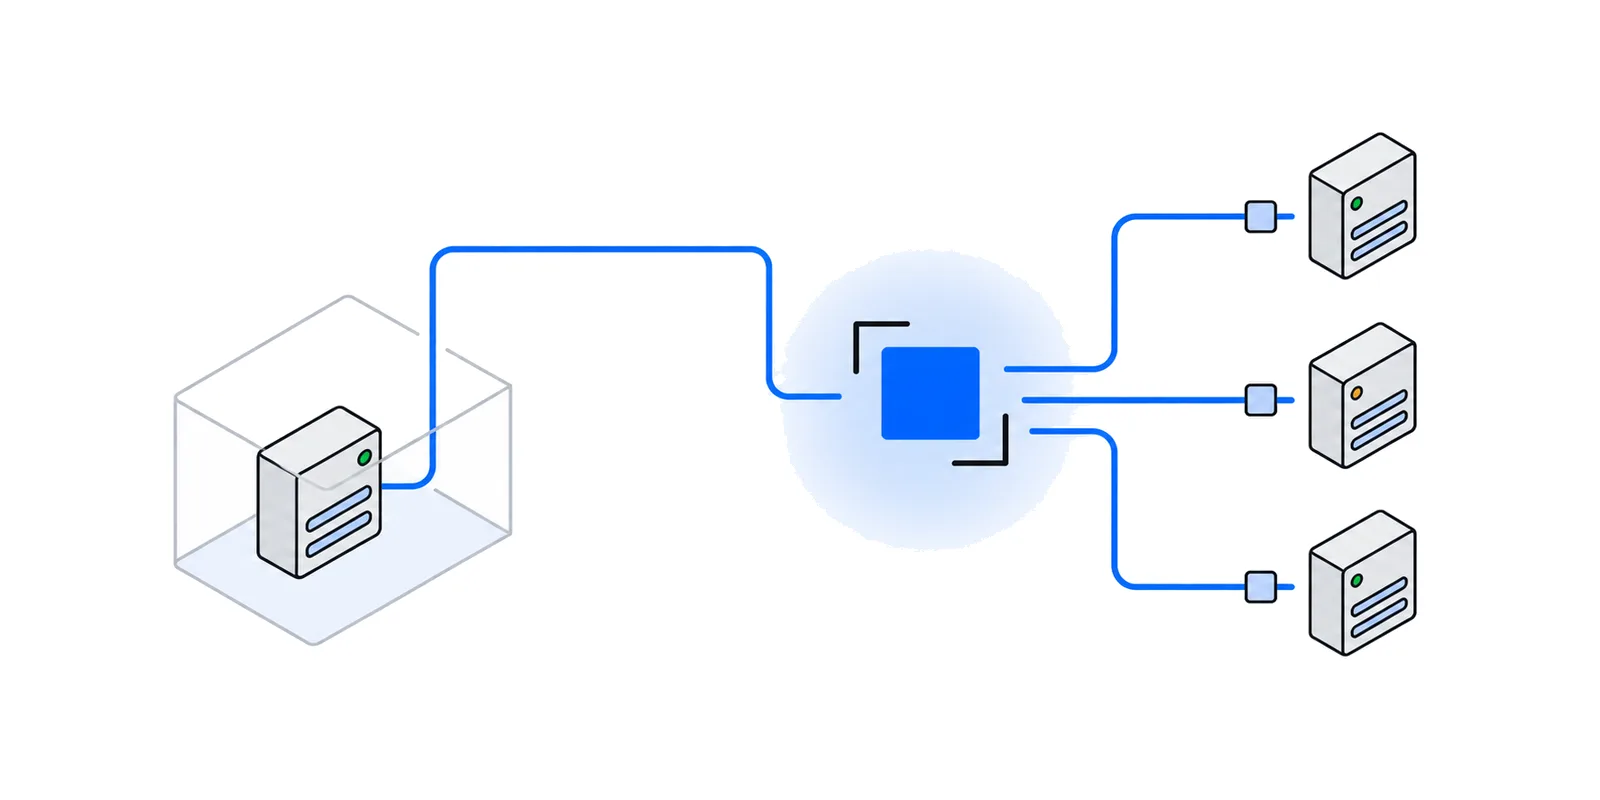
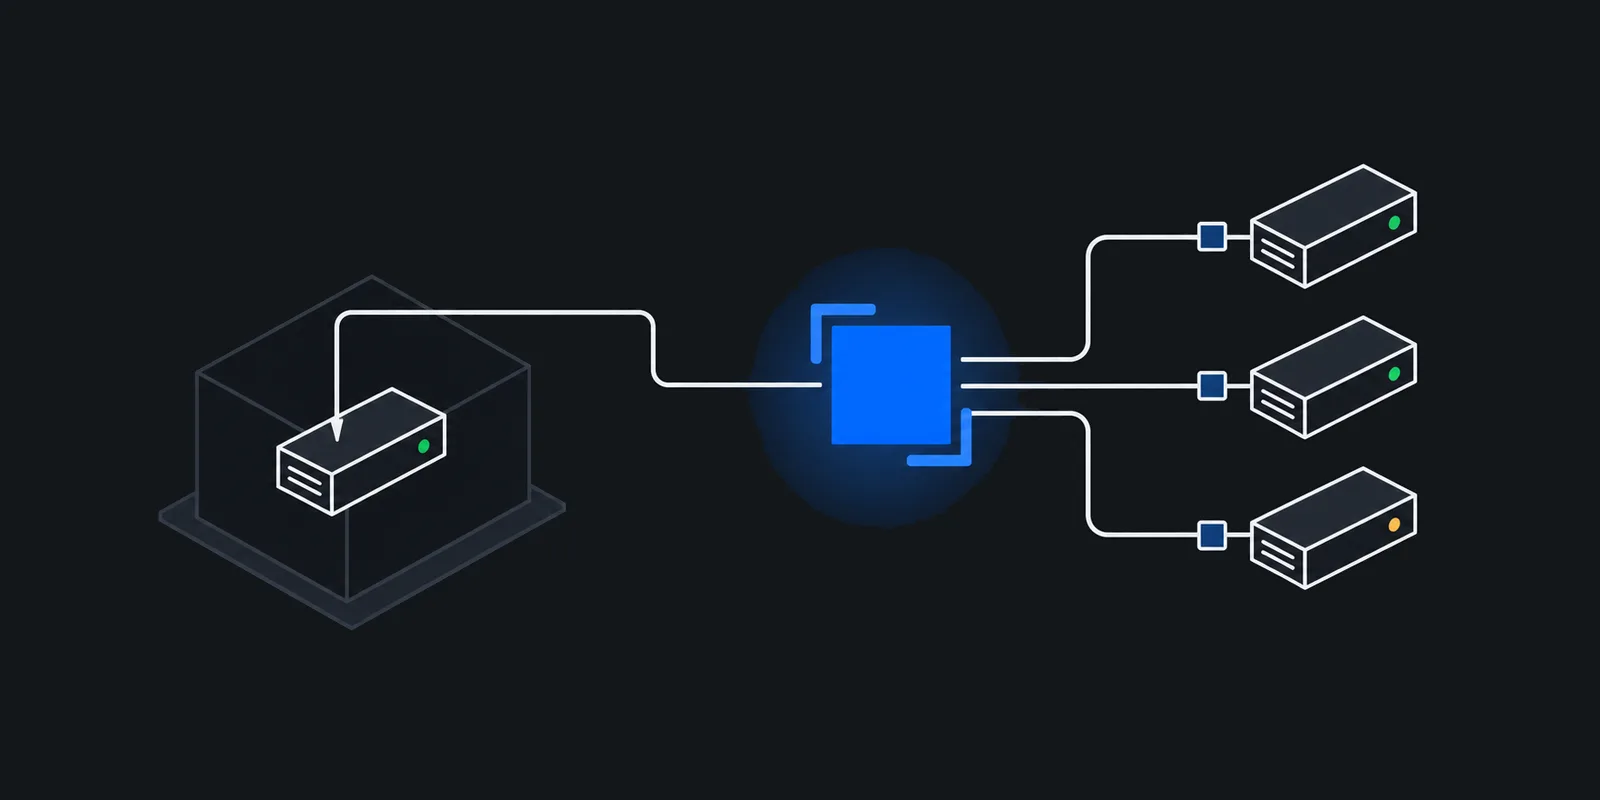
Serve a tunnel from behind NAT with fixedmarkd
Run fixedmarkd on the machine that holds the service, at home, in an office, or behind carrier-grade NAT. It dials out to the route's two ingress IPs on port 443, and partner connections come back down those sessions to a local target such as 127.0.0.1:8080.
- Your machine opens no inbound port.
- For an http route it orders the certificate and keeps the key on your machine.
- Partner lists, metering, and connection logs apply as on any route.
Set up a connector, or read the fixedmarkd reference.
Later
On the roadmap
Planned after launch, in rough priority order.
- On the roadmap
Multi-region failover
Allowlist IPs in two regions and fail over automatically if a region goes down.
- On the roadmap
Terraform provider
Manage apps, IPs, and credentials as code alongside the rest of your infrastructure, on top of the REST API.
- On the roadmap
IPv6 egress and WireGuard
IPv6 egress at no extra cost and a WireGuard tunnel for whole-network routing.
Protocols
Protocols and clients
Every plan includes HTTP and SOCKS5 on the same IPs, so you do not need separate subscriptions. The fm tunnel CLI is included too.
HTTP CONNECT on a TLS endpoint
Set one HTTPS proxy URL. Your client opens TLS to the proxy on port 443, then a CONNECT tunnel to the destination, so proxy credentials are encrypted in transit. The plain HTTP endpoint on port 8080 is for clients that cannot do TLS and sends them in cleartext.
SOCKS5
For databases, SSH, SFTP, and any TCP service. Use socks5h:// so DNS resolves on the proxy side. Plain SOCKS5 on port 1080 sends your token in cleartext. SOCKS5 over TLS on port 1443 encrypts it.
fm tunnel CLI
Port-forward mode maps a local port to a remote host, such as 5432:db.example.com:5432. Transparent mode routes traffic for named hosts with no code changes. It always connects over TLS on port 1443.
Local config file
The CLI reads its routes and token from a local config file. It does not call a Fixedmark API at startup, so a control-plane outage cannot stop your app from booting.
Code for each language is in the docs quickstart.
Architecture
How it works
Each region runs a pair of proxy nodes. Each node owns one of your two static IPs and sends traffic from it.
Health checks run against both nodes. If a node fails, its IP moves to the healthy node. Traffic keeps leaving from the same two addresses, so your allowlist entries stay valid.
IPs are tracked separately from servers. When a node is replaced, the IP moves to the new node. It is never swapped for a new address.
Your IPs live in one region. Multi-region failover is on the roadmap. See launch regions for details.
- 1Your app (Vercel, Railway, Supabase, ...)
- 2Proxy URL over TLS, or SOCKS5
- 3Region: node A + node B, health-checked
- 4Egress from IP 1 or IP 2 (IP failover between nodes)
- 5Partner API or database allowlists both IPs
What Fixedmark does not do
- No rotating or residential proxies. Fixed IPs only.
- No scraping. Abuse on one account can harm IP reputation for everyone else.
- No outbound mail on port 25. See the support docs for mail ports.
- No decryption of your TLS traffic, on any plan.
More on this on the security page.
Works with your platform
Setup guides for each platform:
Frequently asked questions
What does a static outbound IP proxy do?
It sends your app's outbound requests through servers with fixed public IP addresses. The API or database you call sees the same IP pair every time, so you can add those IPs to its allowlist once, even when your app runs on serverless functions with changing IPs.
Is the IP pair shared with other customers?
On Starter and during the trial the IP pair is shared. On plans with dedicated IPs, the pair is reserved for your account and no other customer sends traffic from it. The pricing page names the plans that include dedicated IPs.
Can Fixedmark read my HTTPS traffic?
No. HTTP CONNECT and SOCKS5 pass your TLS connection through end to end. Fixedmark sees the destination host, port, TLS SNI, and byte counts, never the request or response content.
How do I use Fixedmark with a database that has no proxy support?
Use SOCKS5 if your driver supports it. If it does not, run fm tunnel, included on every plan, to forward a local port to the database through your static IPs, for example fm tunnel 5432:db.example.com:5432.
What happens if one node in a region fails?
Each region runs a pair of health-checked nodes. If one fails, its IP moves to the healthy node, so traffic keeps leaving from the same IP addresses you allowlisted.
Which features are available today?
Every feature marked Early access is built and available to early-access accounts, and ships with the first public version. Features on the roadmap are not built yet and come after launch.
Make it fixed.
Fixedmark is in early access. Join the list to get dedicated static IPs when your region opens.